
A 50-person logistics firm in Selangor collects driver ICs, delivery addresses, and payment records every day. Until mid-2025, the worst-case penalty for mishandling that data was RM300,000. That ceiling has now tripled.
The Personal Data Protection (Amendment) Act 2024 was rolled out in three phases between January and June 2025. It aligns PDPA data protection requirements in Malaysia with international standards such as the GDPR, and the obligations are no longer limited to large corporations. Any organisation that processes personal data in the context of commercial transactions is in scope.
The good news: compliance is achievable once you break it into the right steps. In this guide, we cover how to comply with PDPA Malaysia for businesses of any size, from appointing a DPO to building a breach response plan, and where providers of data protection services in Malaysia (like Net Onboard) fit into the picture.
What Changed Under the PDPA Amendment 2024
Malaysia’s PDPA has been in place since 2010, but it wasn’t updated until the 2024 amendment. This marks the first legislative revision since the Act came into force in 2013, and it closes several gaps that left businesses exposed.
Here are the changes that affect daily operations the most:
- Mandatory DPO appointment. Both data controllers and data processors must now appoint a Data Protection Officer. This applies from June 2025 and is not limited to large organisations. SMEs that handle personal data in commercial transactions need a DPO too, though outsourcing the role is permitted.
- 72-hour breach notification. If a personal data breach occurs, the data controller must notify the Personal Data Protection Commissioner within 72 hours. Where the breach is likely to cause significant harm, affected individuals must also be notified within seven days of that initial report.
- Data processor liability. Previously, obligations under the PDPA’s Security Principle only applied to data controllers (formerly called “data users”). Data processors, such as cloud vendors and IT service providers, are now directly accountable for protecting the data they handle.
- Expanded sensitive data definition. Biometric data, including fingerprints and facial recognition records, is now classified as sensitive personal data requiring the highest level of protection.
- Stricter cross-border transfer rules. The old whitelist regime has been replaced with an adequacy-based framework. Businesses transferring personal data overseas must verify that the receiving country provides equivalent protection to the PDPA.
Penalties have increased to match. Non-compliance with the PDPA’s data protection principles now carries fines of up to RM1 million and up to three years’ imprisonment, compared to the previous cap of RM300,000 and two years.
Five Steps to PDPA Compliance
Getting compliant doesn’t require rebuilding your entire IT stack, but it does require knowing exactly what data you hold, who touches it, and what happens when something goes wrong. Here’s a checklist of PDPA’s data protection requirements in Malaysia, broken into five actionable steps.
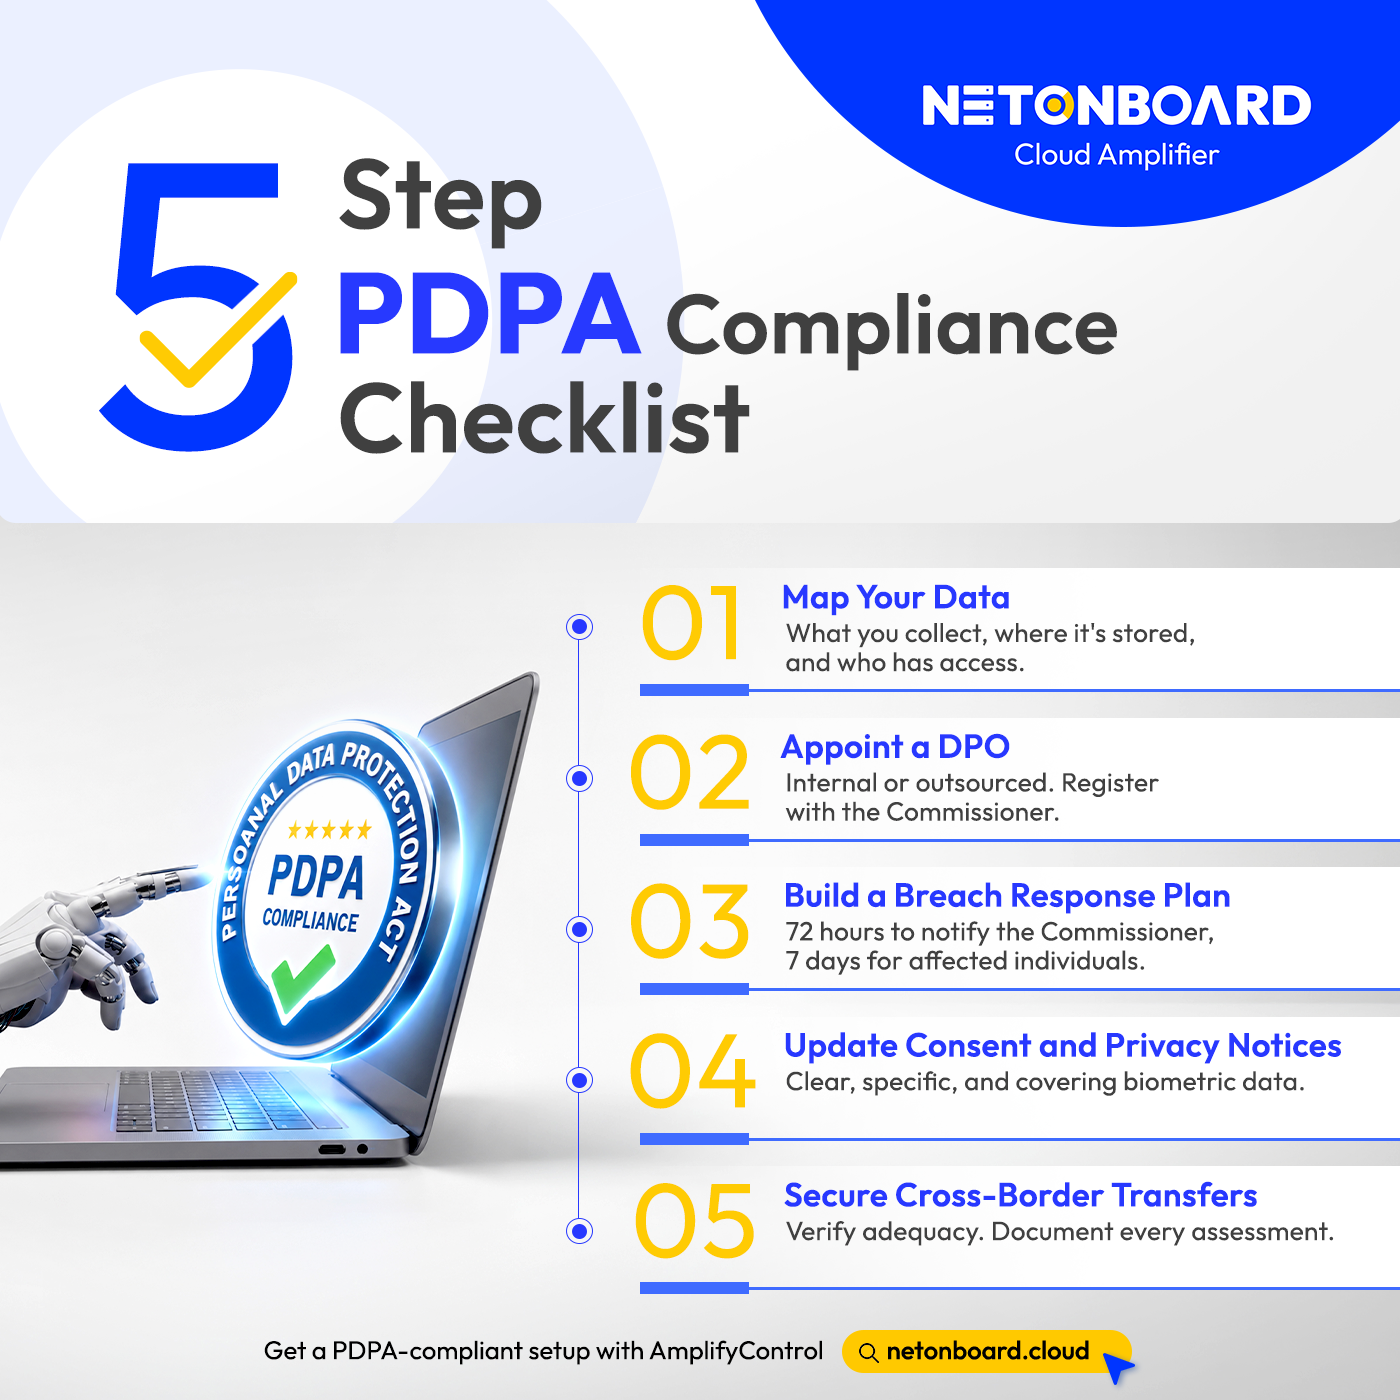
Each of these steps requires visibility into how data moves through your systems. If you’re running workloads on cloud infrastructure, you will need to set your security configuration, access policies, and monitoring stack up correctly from the start to maintain that visibility.
How to Protect Customer Data Under the PDPA in Malaysia
The PDPA’s Security Principle (Section 9) requires organisations to take “practical steps” to protect personal data from loss, misuse, unauthorised access, and accidental disclosure. That’s deliberately broad, and the Commissioner has signalled that enforcement will focus on whether an organisation took reasonable measures relative to the risk.
For most mid-sized businesses, practical protection means getting four things right:
- Access controls. Limit who can view and edit personal data to staff with a legitimate need. Role-based access, multi-factor authentication, and privileged access management should be implemented to significantly reduce the attack surface.
- Encryption. Personal data should be encrypted both at rest and in transit. This is especially critical for sensitive categories like biometric records and financial data.
- Monitoring and detection. Conduct continuous monitoring across endpoints, cloud environments, and network traffic to catch anomalies before they escalate. A breach you don’t know about is a breach you can’t report within 72 hours.
- Retention policies. The PDPA requires that personal data be retained only for as long as it serves its original purpose. Regular audits and automated retention schedules should be performed to prevent data from lingering where it shouldn’t.
Malaysia’s Cyber999 Q1 2025 report recorded data breaches as 8% of all reported incidents, with intrusion cases rising 76% quarter-on-quarter. Those numbers underscore the urgency on the operational side of protection, especially for businesses still relying on manual security processes.
What Non-Compliance Costs Malaysian Businesses
The RM1 million fine is the headline figure, but it’s rarely the full picture. Malaysia’s Digital Minister disclosed in October 2024 that data breach cases jumped from 50 in 2022 to 646 in 2023, a 1,192% increase. By September 2024, another 427 cases had been logged. Enforcement capacity is catching up with the volume.
Beyond regulatory fines, there are real costs across several fronts for not complying with the Act:
- Operational disruption. Investigating breaches diverts your attention from revenue-generating activities. And depending on the severity, regulators can order data processing to stop entirely until remediation is confirmed.
- Personal liability. Directors, managers, and key officers can face individual penalties unless they prove the breach occurred without their knowledge, consent, or negligence, and that they took all reasonable precautions.
- Customer trust. For consumer-facing businesses, a breach that’s made public erodes the trust that took years to build. In the case of a data incident, the even higher cost is customer churn, in addition to the fine itself.
The financial services sector carries additional exposure, since banks and insurers already fall under Bank Negara’s Risk Management in Technology (RMiT) framework. For these organisations, PDPA non-compliance is a second regulatory layer on top of existing obligations.
Get PDPA-Ready With the Right Support
Most businesses don’t struggle with understanding the PDPA requirements. The challenge is implementing them consistently across cloud environments, endpoints, and internal processes, then maintaining that posture as the business scales.
If you’re running cloud workloads with personal data, managing cross-border data transfers, and/or lack a breach detection and response workflow that meets the PDPA’s requirements, it’s best to get started with a managed data protection approach sooner rather than later.Cue Net Onboard, where our AmplifyControl pillar covers the operational side of how to protect customer data under the PDPA in Malaysia. It’s built for businesses that need their cloud environments secured and governed to meet regulations like the PDPA, without building an in-house security team from scratch.
Find out how our data protection services in Malaysia can support your PDPA compliance today, from access management and encryption through to continuous threat monitoring. Talk to our team to see how we can help.